
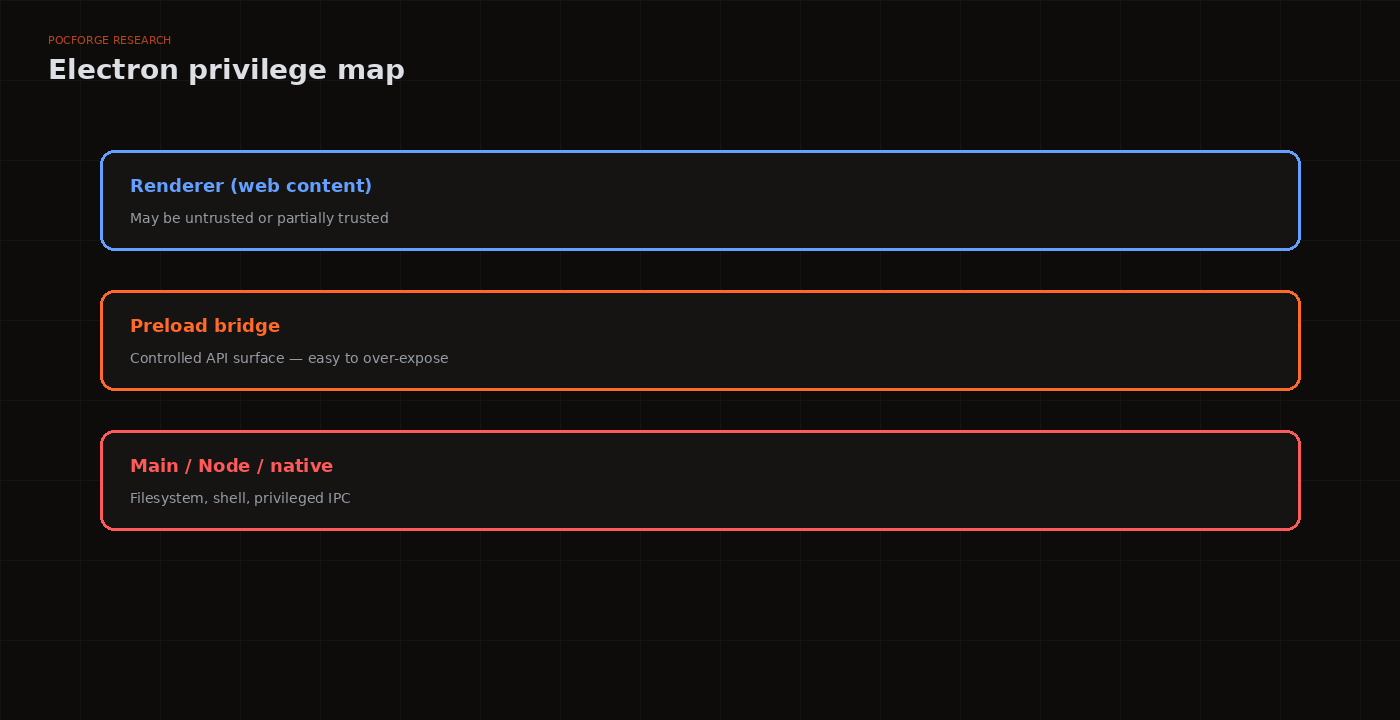
Electron applications combine browser content with desktop capabilities. That architecture is powerful, but it creates a security boundary between potentially untrusted renderer content and privileged Node.js or native capabilities. A secure assessment therefore needs to follow data across the renderer, preload bridge, IPC handlers and filesystem/process APIs rather than testing each component independently.
1. Build the privilege map
Inventory windows, webviews, preload scripts, custom protocols, deep links, IPC channels, file import/export, plugin systems and update mechanisms. Record which code executes with Node.js privileges and which origins can reach it.
| Boundary | What to inspect | Security question |
|---|---|---|
| Renderer → preload | contextBridge APIs | Are exposed methods minimal and validated? |
| Renderer → IPC | ipcMain handlers | Does each handler authenticate and authorise the request? |
| Input → filesystem | paths, archives, imports | Can attacker-controlled names escape intended directories? |
| URL → navigation | deep links, external URLs | Can untrusted URLs reach privileged content? |
2. Test renderer isolation
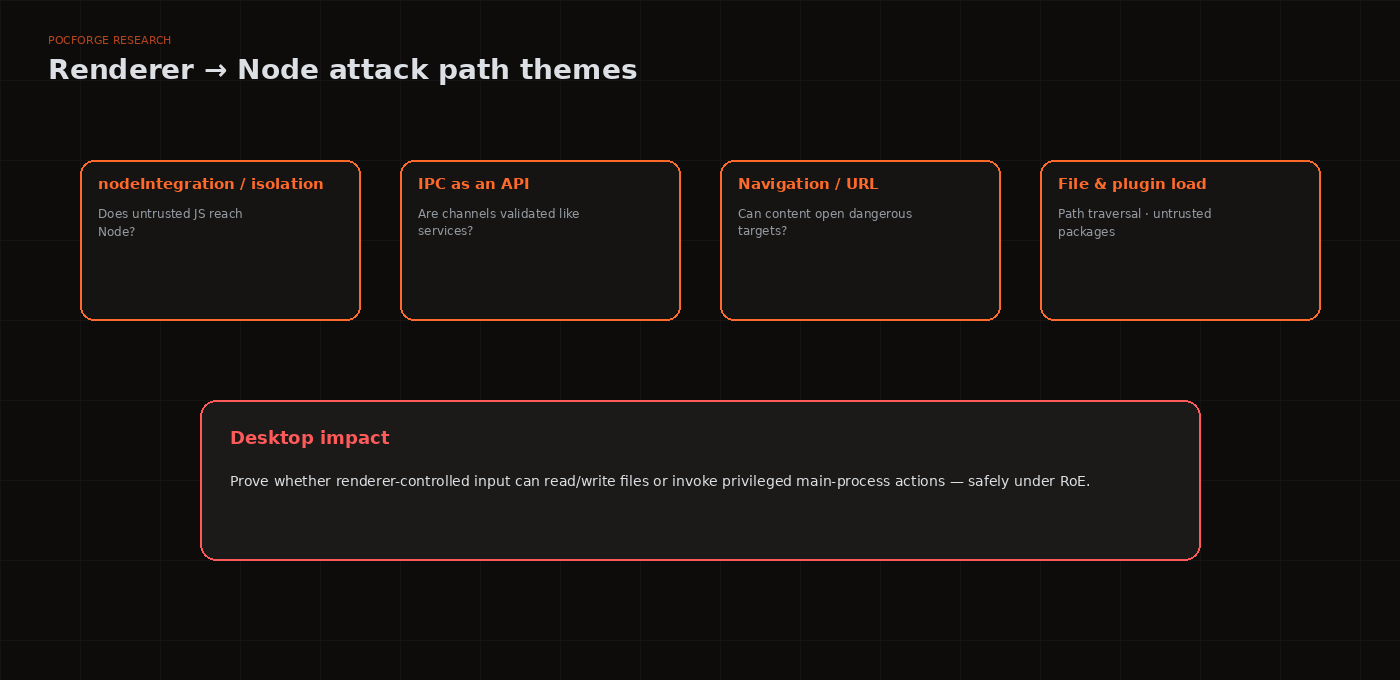
Review security-sensitive BrowserWindow settings and verify that the renderer cannot directly obtain Node.js primitives. Then inspect whether a preload bridge accidentally exposes powerful functions such as arbitrary command execution, filesystem access, unrestricted HTTP requests or dynamic module loading.
Renderer input
   ↓
DOM / JS
   ↓
Preload API
   ↓
IPC handler
   ↓
Node / filesystem / process
3. Attack IPC as an API
List IPC channels and treat each handler like a private API endpoint. For every channel, identify the accepted arguments, caller context, sensitive actions and validation. Test type confusion, path traversal, arbitrary URLs, unsafe object merging and authorisation assumptions.
Keyboard: ← → · Respects reduced-motion (no autoplay).
IPC threat model
4. File and plugin handling
Archive extraction and plugin installation deserve special attention. Test path normalisation, absolute paths, traversal sequences, symlink behaviour, package metadata and destination directory controls. Verify that uploaded or downloaded content cannot write outside an intended sandbox.
For plugin ecosystems, also review signature verification, origin trust, update channels and whether plugin code receives more privileges than necessary.
5. Prove desktop impact safely
Use a controlled proof such as writing a harmless marker file, invoking a benign application or demonstrating access to a test directory. The objective is to establish the trust-boundary failure without causing destructive behaviour.
6. Hardening checklist
- Keep renderer contexts isolated from Node.js capabilities.
- Expose the smallest possible preload API.
- Validate IPC arguments server-side in the main process.
- Restrict navigation and external content.
- Normalise and constrain filesystem paths.
- Verify plugin provenance and integrity.
- Keep secrets out of renderer-accessible storage and logs.
- Maintain Electron and bundled dependencies.
Why this matters
Electron security is often misclassified as “just configuration.” In practice, the highest-value findings frequently emerge from how several individually reasonable features interact: an import feature, a preload method, an IPC handler and a privileged filesystem operation can form a complete attack path.
Related: Desktop / Electron penetration testing · Electron PT series (Parts 1–6) · Business logic flaws · All research.
Frequently asked questions
Why is Electron a special desktop risk?
It combines a web renderer with powerful Node capabilities. If isolation fails, web content can reach filesystem or shell impact.
What is the preload bridge for?
A controlled API surface between renderer and privileged code. Over-exposing Node or IPC turns the bridge into an attack path.
Is disabling nodeIntegration enough?
It is necessary but not sufficient. Review contextIsolation, sandbox, navigation, IPC validation and permission handlers together.
What should a desktop assessment prioritise?
Trust boundaries between remote/untrusted content and privileged APIs—not only dependency CVEs.
