
VAPT services in India for startups and growing organisations
Scope-based vulnerability assessment and penetration testing across web, API, mobile, cloud, network and AI — with validated findings, clear evidence and a retest of up to 10 issues within 6 months of the original test. Built for Indian SaaS, fintech and product teams that need practical security testing, not a scanner dump.
-
Scope-based quoteConfirmed after a short scope review
-
Retest includedWithin 6 months of the test
-
Remote deliveryFor India-market and international teams
-
Vulnerability assessment
Structured discovery of weaknesses across applications, APIs, infrastructure and cloud environments within an agreed scope.
-
Penetration testing
Manual validation of realistic attack paths so findings reflect what an attacker could actually achieve.
-
Remediation retest
After you fix priority issues, we retest and update closure status so engineering and security stay aligned.
What VAPT means for Indian buyers
In India, buyers often search for “VAPT” as a combined phrase covering both vulnerability assessment and penetration testing. A useful engagement does more than list CVSS scores: it explains exploitability, business impact and a practical fix path. PoCForge is a human-led boutique. We use targeted automation where it helps coverage, then spend the engagement validating attack paths — authentication, authorisation, business logic, tenant isolation, cloud identity and perimeter exposure — depending on the surfaces you put in scope.
We publish indicative India pricing on our penetration testing cost guide and starting prices on the pricing page. Final quotes always follow a short scope review so you are not locked into a package that does not match your attack surface.
Service areas we cover
Most India VAPT programmes combine more than one surface. Choose what matches your product risk:
- Web application penetration testing — auth, sessions, authorisation, business logic, injection and file handling.
- API security testing — REST/GraphQL, BOLA, mass assignment, data exposure and workflow abuse.
- Mobile application penetration testing — Android/iOS client and API-backed flows.
- Cloud security assessment — identity, exposure, misconfiguration and attack paths in AWS/Azure/GCP scopes.
- External infrastructure penetration testing — internet perimeter, DNS, email auth, VPN and cloud edge.
- Desktop / thick-client penetration testing — Electron and classic desktop apps, IPC and local privilege boundaries.
- Network & Active Directory pentesting — internal identity and lateral movement objectives.
- AI / LLM security testing — prompt/tool abuse, agent permissions and data exfiltration paths.
See the full map on Solutions. India-specific landing pages also exist for several surfaces when you need locale-focused copy for stakeholders.
Indicative India pricing
Examples from our published ranges (exclusive of GST; final quote is scope-based):
- Web application: ₹30,000 – ₹65,000
- Web + API: ₹55,000 – ₹1,10,000
- API security: ₹25,000 – ₹60,000
- Mobile (per platform): ₹35,000 – ₹80,000
- External network / infrastructure: ₹25,000 – ₹65,000
- Desktop / thick client (Electron): ₹40,000 – ₹95,000
- Cloud security review: ₹35,000 – ₹90,000
- Internal / Active Directory: ₹55,000 – ₹1,35,000
- AI / LLM security testing: ₹45,000 – ₹1,10,000
- Application bundle (app + mobile): ₹90,000 – ₹1,75,000
Full bands and cost drivers: Penetration testing cost in India 2026. Starting prices by service are on the pricing page.
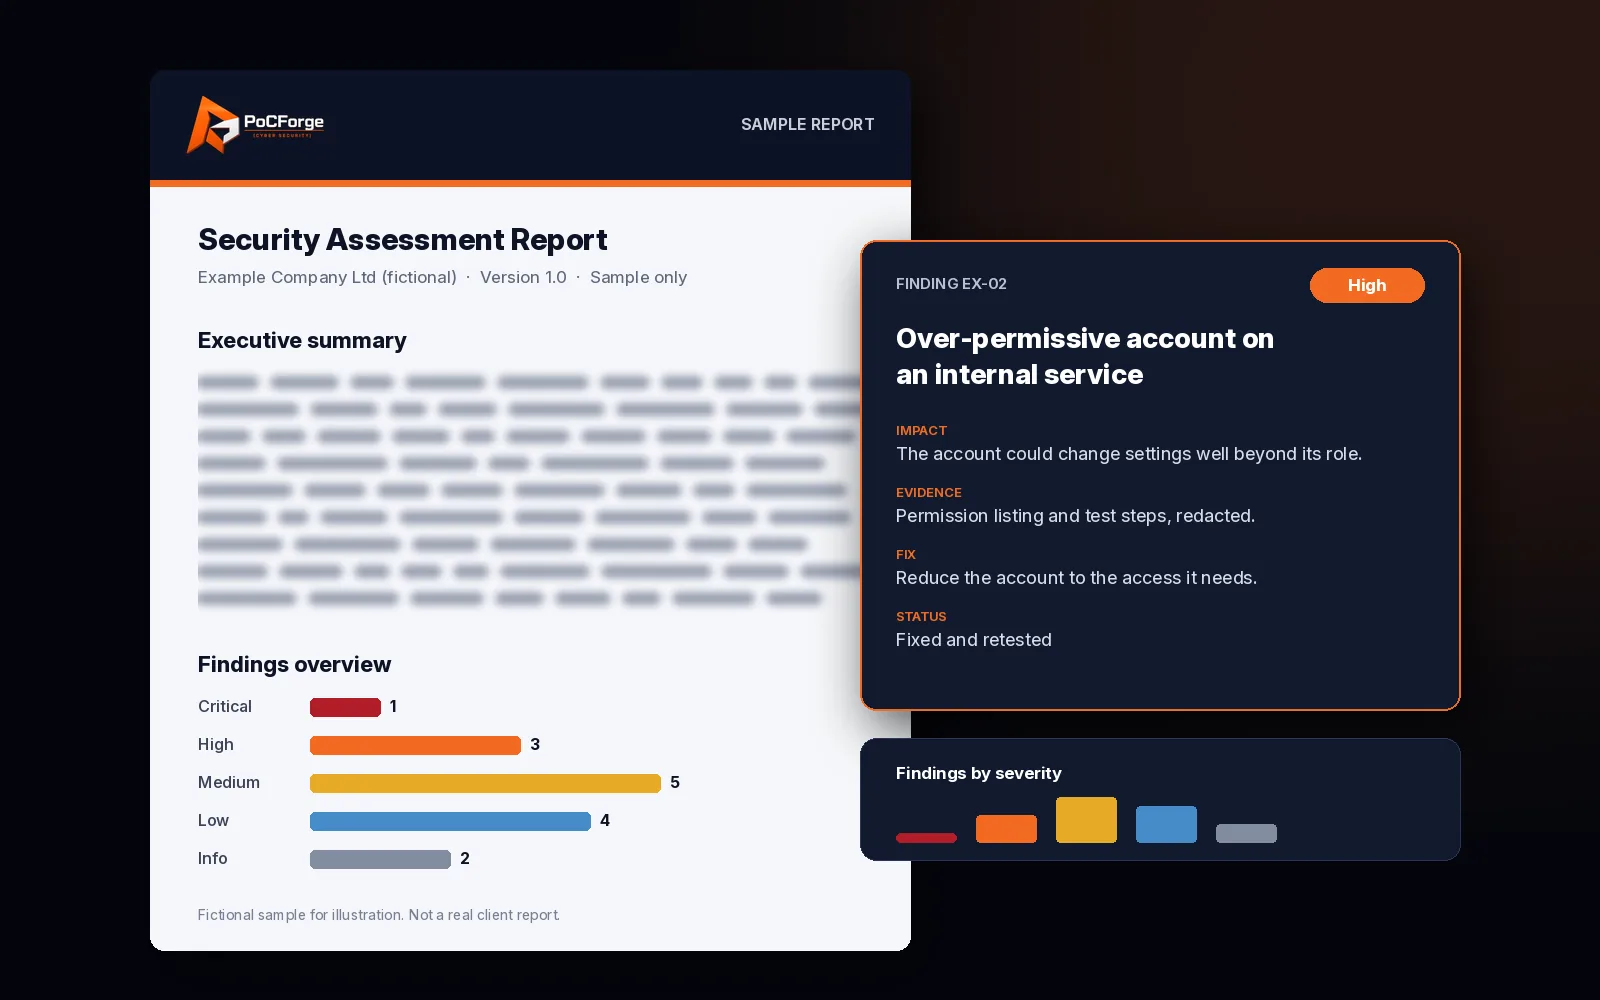
Deliverables you can hand to customers and auditors
- Executive summary for leadership and customer security questionnaires
- Technical findings with evidence and reproduction detail
- Remediation guidance aimed at engineering owners
- Retest notes / closure status for fixed items in scope
We do not publish confidential exploit detail or client names without permission. See anonymised patterns in case studies.
VAPT vs penetration testing vs vulnerability scanning
These terms are used loosely in the market. A clear buyer model:
- Vulnerability scanning — automated discovery of known issues and misconfigurations. Fast, useful for hygiene, high noise if used alone.
- Vulnerability assessment — organised review and prioritisation of weaknesses, often still heavier on tooling with analyst triage.
- Penetration testing — adversarial testing that attempts to validate exploitation and chained impact under agreed rules of engagement.
- VAPT (India usage) — typically a commercial bundle of assessment plus pentest-style validation and a formal report.
PoCForge engagements lean toward validated penetration testing with assessment coverage of the agreed surface. If you only need a compliance checkbox scan, say so early — we will tell you when a lighter option is enough, and when it is not.
Who this is for — and who should look elsewhere
Good fit: Indian and international SaaS/product companies, startups preparing for enterprise security reviews, teams needing SOC 2 / ISO 27001 evidence of testing with clear reports, and organisations that want transparent INR/USD scoping.
May not be the right fit: regulated banking, insurance or government programmes that contractually require a CERT-In empanelled auditor. Empanelment status is a legal/procurement requirement for some buyers — not a substitute for testing quality. Read our guide: Do you need CERT-In empanelled VAPT? Always verify the official CERT-In list before you rely on any vendor’s claim.
Typical India VAPT scenarios
Pre-enterprise sales. A SaaS team preparing for a customer security questionnaire needs a current web+API test, a readable executive summary, and remediation evidence. Depth matters more than an enormous finding count.
Release hardening. Before a major launch or architecture change, teams want focused testing on new auth flows, admin panels and payment-adjacent workflows.
Recurring programme. Quarterly or twice-yearly testing on a defined product slice, with findings tracked to closure. Consistency beats one-off panic tests.
Perimeter + app. Product security plus external infrastructure coverage when public IPs, VPN or cloud edge are part of the story customers ask about.
What “good” looks like in a VAPT report
Useful reports make prioritisation obvious: which issues enable account takeover, data exposure across tenants, privilege escalation, or remote compromise of perimeter services. Each high-impact finding should be reproducible by your engineers without guesswork. Low-signal scanner noise should be filtered or clearly labelled. Retest notes should show what changed after remediation.
If a vendor cannot explain an issue in product terms — who is affected, what data moves, what control failed — treat that as a quality signal during vendor selection.
Frequently asked questions
What is included in PoCForge VAPT?
An agreed scope of vulnerability discovery and manual validation, a written report with evidence and remediation guidance, and a retest of up to 10 issues within 6 months of the original test.
How long does a typical engagement take?
Small web or API scopes often complete in days to a couple of weeks including reporting. Larger multi-surface programmes take longer. Timeline is confirmed during scoping.
Do you only use automated scanners?
No. Tooling helps coverage; reported issues are manually validated with proof-of-exploit style evidence wherever safe and authorised.
Can you support remote testing for India and international teams?
Yes. PoCForge is based in Delhi (NCR). Most engagements are remote, across India and internationally, with on-site in India when a scope needs it. India and global starting prices are on the pricing page.
Are you CERT-In empanelled?
Do not assume empanelment from marketing pages. If your contract requires CERT-In empanelment, verify the current official CERT-In empanelled organisations PDF and match the legal entity name. PoCForge publishes a decision guide for SaaS vs regulated procurements.
How do we start?
Use the contact page with a short description of assets, environments and timeline. We reply with clarifying questions and a scope-based quote.
Related PoCForge guides
Related India guides
Need a scope-based estimate?
Share your application, infrastructure or security requirement and PoCForge will help define the right assessment.
