
Penetration testing company in India
PoCForge delivers human-led penetration testing for Indian SaaS, fintech and product teams — attack-path validation, clear reports and retesting. Remote engagements for India and international organisations.
-
₹30,000 – ₹65,000Indicative web app band, + GST
-
Scope-based quoteConfirmed during scoping
-
Retest includedIn-scope fixes checked again
-
Remote deliveryFor India-market and international teams
-
Manual-first testing
Security professionals validate attack paths rather than shipping untriaged scanner output.
-
Scope-based pricing
Published INR ranges help you plan; the final quote stays tied to the actual attack surface.
-
Actionable reporting
Findings include reproduction steps, evidence, impact and remediation guidance your engineers can use.
A boutique built for modern product stacks
PoCForge is an offensive-security practice focused on how modern organisations actually ship software: multi-tenant SaaS, API-heavy backends, cloud identity, mobile clients and increasingly AI-assisted workflows. We are not a scanning platform reseller. Engagements are scoped with you, executed by practitioners, and closed with evidence and a retest.
Learn more on our About Us page, browse solutions, or read technical write-ups in research.
What we test
- Web applications — authentication, authorisation, business logic and chained exploits.
- APIs — BOLA, privilege boundaries and data exposure.
- Mobile apps — client storage, transport and API-backed abuse cases.
- Cloud — exposure, IAM and misconfiguration attack paths.
- External infrastructure — perimeter hosts, DNS, email auth, VPN and edge.
- Internal / Active Directory — identity and lateral movement objectives.
- AI / LLM systems — agent permissions, prompt/tool abuse and sensitive data paths.
Pricing transparency
Indicative India ranges are published on the 2026 cost guide and summarised under VAPT services India. Example planning band for a typical small-to-medium web application: ₹30,000 – ₹65,000 + GST. See the pricing page for starting prices by service.
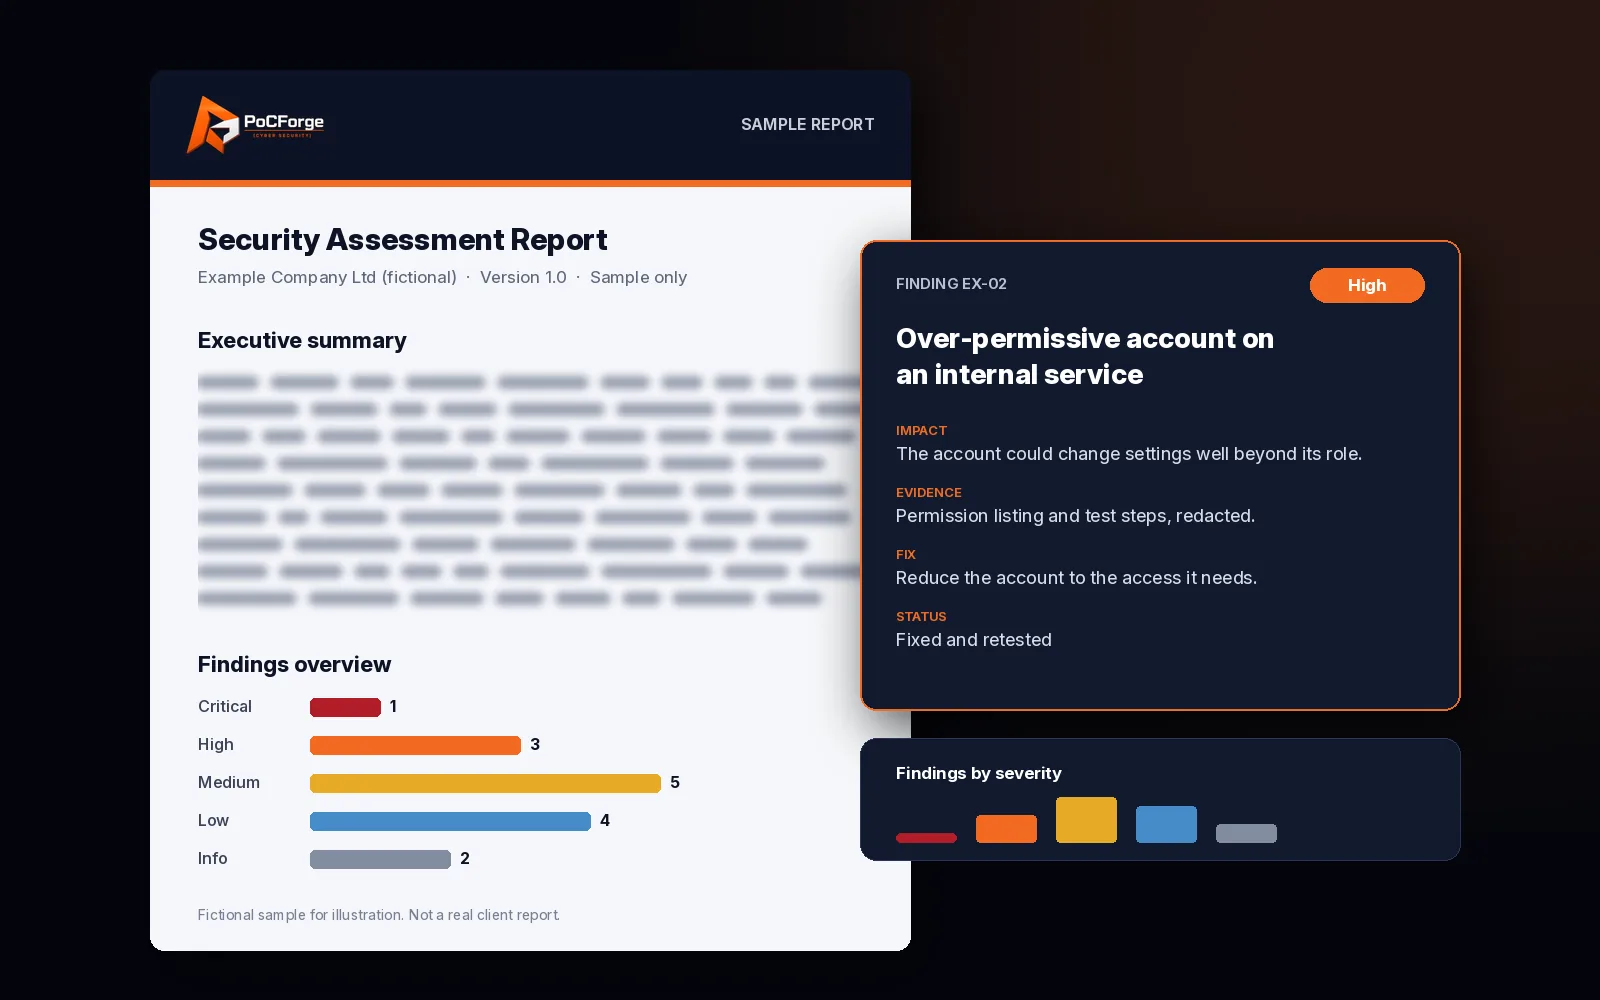
Deliverables and communication
Every engagement produces a written report with an executive view and technical detail. We prefer early clarification over surprise findings at the deadline. If a critical issue appears during testing, we escalate through the contacts named in the rules of engagement so you can begin containment while the rest of the test continues.
After delivery, the remediation retest is a first-class part of the engagement — not an upsell surprise. Closure status for retested items is documented so customer reviews and internal trackers stay accurate.
India compliance conversations
Indian RFPs and enterprise questionnaires often mention CERT-In, RBI, SEBI, IRDAI or DPDP. Those regimes are not identical, and “CERT-In empanelled” is a specific procurement status — not a universal quality medal. If your buyer contractually requires an empanelled organisation, you should verify the official CERT-In list and choose accordingly. If you need rigorous manual testing for a SaaS product and SOC 2 / ISO-style evidence, a capable non-empanelled boutique may be the better technical fit. Our guide: Do you need CERT-In empanelled VAPT?
Proof of work
We publish anonymised engagement patterns in case studies and deep technical research so you can judge how we think.
Industries we commonly support
SaaS and technology product companies, financial platforms (application/API focus — not a substitute for regulator-mandated empanelled audits when those apply), healthcare/healthtech applications, e-commerce and consumer platforms, and enterprise product security teams needing specialist offensive support. See also VAPT services India.
Why teams choose a human-led boutique
Platform scanners and continuous DAST have a place. They do not replace someone who can reason about multi-step authorisation flaws, tenancy bugs, or unsafe AI tool permissions. PoCForge sits in that specialist lane: shorter communication paths, proof-focused findings, and pricing you can plan against.
If you are weighing a boutique against a large consultancy, read Boutique vs Big-Four VAPT in India first.
Remote testing across time zones
Most PoCForge work is remote. That suits distributed product teams in India and overseas buyers who need English-language reports and clear scheduling. Testing windows can favour off-peak hours for production-sensitive checks. India-market INR pricing and international USD pricing are both supported at the scoping stage.
Next steps
1) Skim solutions and pick surfaces. 2) Check planning bands on the cost guide. 3) Send a short brief via contact. 4) If a questionnaire mentions CERT-In, read the decision guide before you lock vendor criteria.
Frequently asked questions
Is PoCForge based in India?
Yes. PoCForge is based in Delhi (NCR) and works remote-first with India-market and international buyers. City pages are local buyer context, not separate city companies. On-site in India is planned when a scope requires it. The pricing page shows starting prices for India (INR) and global (USD) clients.
Do you provide certificates after testing?
We provide professional reports and retest confirmation suitable for many customer and compliance evidence requests. Wording of any “certificate” should match what your auditor or customer actually accepts — ask us if you are unsure.
Can you test production?
Often yes, under strict rules of engagement. Many teams prefer staging plus limited production checks. We agree environments before testing starts.
How do you handle confidentiality?
Engagements are confidential under the statement of work / NDA as agreed. We do not publish client names or exploit detail without permission.
Where should I start?
Send a short scope via the contact page or compare surfaces on Solutions.
Related PoCForge guides
Related India guides
Ready to scope a penetration test?
Tell us what you are building and the security questions you need answered.
