
GCP security assessment
A human-led review of your GCP projects: identity and access, network exposure, compute and data stores, keys and secrets, and logging — combined with attack-path testing that shows what a compromised identity or exposed service could actually reach.
- Read-only review
- Attack paths, not just a benchmark
- Retest included
-
Read-only accessA role you create and revoke
-
Sized to scopeDates agreed after the scope call
-
Retest includedWithin 6 months, up to 10 issues
-
Walkthrough callEvidence, steps and fixes
Who this is for
A good fit
- Organisations running production or staging workloads in GCP who want more than a benchmark export.
- Useful before a major release, after an organisation restructure, when onboarding a new account model, or when a customer or auditor asks for evidence of a cloud penetration test.
What we test
Identity and access
IAM bindings and custom roles
Details
- IAM bindings and custom roles
- Service accounts and keys
- Workload identity and federation
- Privilege-escalation paths between service accounts
- Domain-wide delegation and admin roles
Network and exposure
Public endpoints and internet-facing services
Details
- Public endpoints and internet-facing services
- VPC firewall rules and hierarchical policies
- Shared VPC and Private Google Access
- Exposed management ports and open databases
Compute and containers
Compute Engine configuration and metadata
Details
- Compute Engine configuration and metadata
- Google Kubernetes Engine and Cloud Run
- Cloud Functions permissions
- OS Login and serial-console access
Data stores
Cloud Storage bucket IAM and public access
Details
- Cloud Storage bucket IAM and public access
- Cloud SQL and other database exposure
- Backup and snapshot sharing
Keys and secrets
Cloud KMS key policies
Details
- Cloud KMS key policies
- Secret Manager exposure
- Secrets in images or pipelines
Logging and detection
Cloud Audit Logs coverage
Details
- Cloud Audit Logs coverage
- Security Command Center findings that matter
- Organisation-level logging sinks and exclusions
Organisation guardrails
Organisation, folders and projects
Details
- Organisation, folders and projects
- Organisation policies
- Shared VPC and project boundaries
About this scope
Scope is sized to the GCP services you run across the projects you name. We use the GCP security benchmark and CIS-aligned control language as a checklist for coverage, then validate what matters with a tester. Findings are ranked by what an attacker could reach, not by a benchmark score.
What you receive
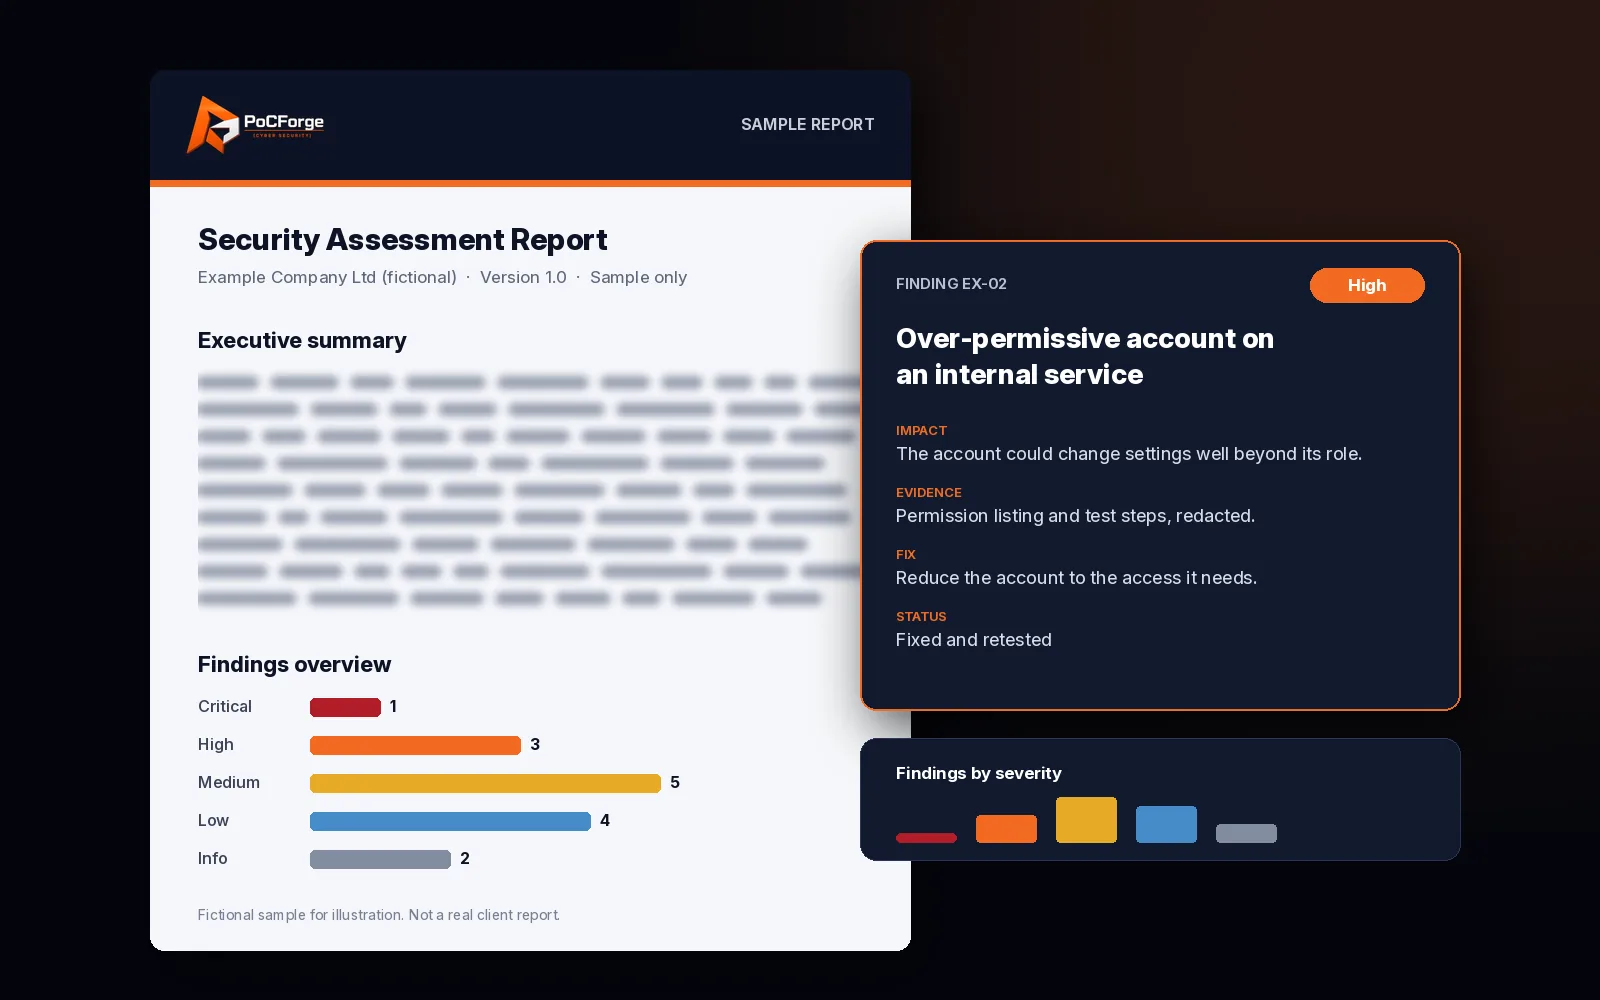
- An executive summary written for non-specialists.
- Technical findings with evidence and steps to reproduce.
- Severity based on what a realistic identity could reach.
- Remediation guidance mapped to the owning team (identity, network, platform).
More about the report
- A walkthrough call.
- A retest of in-scope fixes that are ready within 6 months of the original test (up to 10 issues), with an updated closure note.
Attack paths, not only misconfigurations
Read more
A public bucket is a finding. A service account key on a VM that can impersonate a project-level admin is a path. We map those paths across projects and folders, including Shared VPC and organisation policy gaps, then recommend the smallest change that breaks the chain.
Security Command Center findings are treated as input. We keep what matters, drop noise and add paths the tooling did not assemble.
Common findings (examples)
- An identity with more privilege than its job needs, or a path from a low-privilege role to administrator.
- Storage buckets or databases reachable from the internet without a good reason.
- Security groups or firewall rules that leave management ports open to the world.
- Long-lived access keys or secrets in instance metadata, pipelines or code repositories.
- Logging turned off, or alerts that would not fire on the paths an attacker actually uses.
What we need from you
- List of in-scope projects (and organisation or management structure if used).
- Read-only access for the review role, created by you and revoked when we finish.
- A named contact for production change windows and out-of-scope services.
- Architecture notes or diagrams if you have them (helpful, not required).
Typical timeline
Duration depends on how many projects and services are in scope. A single project with a focused service set is often a short engagement; a multi-project organisation with containers, data stores and custom identity federation takes longer. Dates are agreed after the scope call.
Standards and method
Coverage is guided by Google’s cloud security foundations and CIS-aligned GCP controls, then validated by a tester. Assessment practices follow NIST SP 800-115.
Depth by service family
- IAM. Bindings, custom roles, service accounts and keys, workload identity, domain-wide delegation.
- Network. VPC firewalls, hierarchical policies, Shared VPC, Cloud NAT, public load balancers and open databases.
- Compute. Compute Engine metadata and OS Login, GKE RBAC and node identity, Cloud Run and Cloud Functions permissions.
- Data. Cloud Storage IAM and public access, Cloud SQL exposure and encryption, backups and snapshots.
- Keys. Cloud KMS, Secret Manager, and secrets found in images or pipelines during the review.
- Detection. Cloud Audit Logs, Security Command Center findings that matter, organisation sinks and exclusions.
What stays out of scope by default
- Changing IAM or firewall rules (review is read-only).
- Projects or folders you did not name.
- Denial-of-service against production.
- Google Workspace admin review unless you add it as a separate scope.
Multi-project and Shared VPC notes
Many GCP estates span folders and a Shared VPC host project. We treat that as one attack surface when you name it in scope: a weak binding in a spoke project that can reach a host-project network or a central secret is reported as a path, not as three unrelated ticks on a checklist.
Service account keys and workload identity
Long-lived service account keys remain a common path into GCP. We look for keys that still exist, where they are stored and what they can do, and we prefer findings that push you toward short-lived workload identity where it fits. The report explains the blast radius in project terms your owners already use.
Scope and rules
- Scope call. Projects, services in use, production limits and any services that must not be touched.
- Read-only access. You grant a least-privilege review role. We confirm it before testing starts.
- Configuration review. Identity, network, compute, data, keys and logging against the GCP security benchmark and common CIS control language.
- Attack-path analysis. From realistic starting identities (a developer role, a compromised workload identity, an over-permissive service account), we map what could be reached.
- Controlled validation. High-risk paths are checked safely where agreed. Destructive actions stay out of scope.
- Report and retest. Findings with evidence, a walkthrough and a retest of fixes that are ready within 6 months of the original test (up to 10 issues).
Cloud identity attack-path review
Anonymised cloud identity attack-path pattern: role chains, workload identities and data reachability — finding classes only.
Read the case study →- Read-only review
- Attack paths, not just a benchmark
- Retest included
Related
Frequently asked questions
Is this just a benchmark scan of GCP?
No. Tooling helps with coverage, but findings are checked by a tester and ranked by what an attacker could reach, not by a benchmark score.
What access do you need?
Read-only access to the in-scope projects. Any active testing is agreed separately in writing.
Can you cover more than one cloud?
Yes. Multi-cloud work can be scoped together through the cloud security assessment.
Will you change anything in our accounts?
No. The review is read-only. Controlled validation uses agreed test resources or stop points.
Do you test containers and serverless?
Yes, when those services are in the named scope.
How is this different from the multi-cloud assessment?
This page is GCP-only. The multi-cloud assessment covers AWS, Azure and GCP together.
Does the report help with SOC 2 or ISO 27001?
Yes, as evidence that cloud controls were tested. It does not replace the auditor.
Do you need Organisation Admin?
No. Read-only organisation and project roles are enough for the review.
Ready to scope this?
Tell us what is in scope and what you want to learn. We reply with a suggested approach.
Request a free scope review →