Architecture security assessment
Anonymised pattern: architecture and design review for HealthTech or multi-tenant SaaS — trust boundaries and data flows before implementation debt hardens.
At a glance
-
SectorHealthTech / multi-tenant SaaS
-
SurfacesArchitecture, data flows, control map
-
Duration classDesign / architecture review
-
RetestDesign follow-up checkpoint
Context / challenge
A HealthTech (or multi-tenant SaaS) team wanted security input while major design decisions were still movable: data partitioning, identity model, integration boundaries and logging. The goal was to catch structural issues before a late-stage pentest could only report them as expensive rework.
This sits under security assessments / architecture review within Solutions, often paired later with web, API or cloud testing.
Engagement shape
Typical shape: workshop-led review of architecture diagrams, data-flow descriptions and control intent; threat scenarios aligned to the sector (e.g. sensitive health data, tenant isolation, third-party integrations); written findings as design risks with recommended control patterns — not exploit payloads.
Approach
Read the steps as text
-
Step 1
Discover
Capture architecture, data classes, trust boundaries and integration map.
-
Step 2
Validate
Walk abuse cases against the design with architecture owners.
-
Step 3
Prove
Document design-risk classes with concrete control recommendations.
-
Step 4
Remediate
Adjust design and control intent while change is still cheap.
-
Step 5
Retest
Design checkpoint or later build-time test to verify landing.
Finding classes (illustrative)
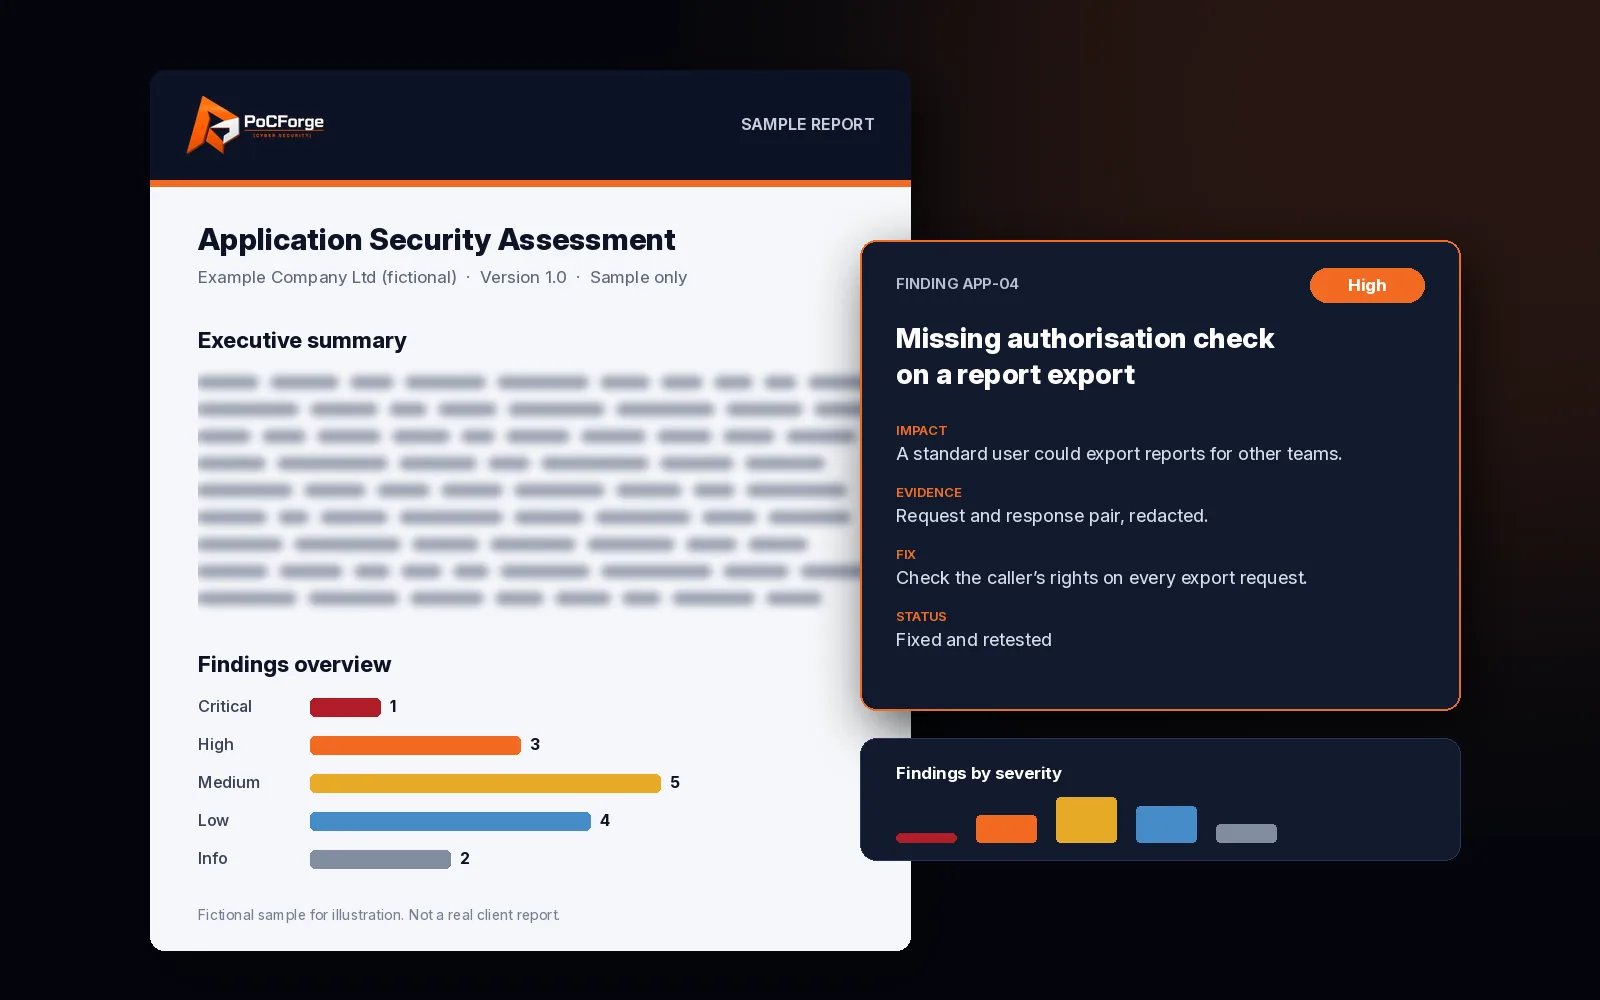
Illustrative design-risk classes: unclear tenant or patient-data binding; over-trust of internal networks; third-party integrations without abuse cases; secrets and key management gaps; missing abuse-case logging; environments that collapse prod-like controls in staging.
Outcomes and remediation pattern
Architecture owners leave with prioritised design changes, a clearer control map, and a backlog that later pentests can verify. If a framework is in scope, we map findings to control intent.
Lessons for buyers
- Buy architecture review early when isolation and data-flow decisions are still cheap to change.
- Ask for abuse cases, not only component inventories.
- Plan a later build-time pentest to verify the design landed.
- Keep public case studies anonymised — diagrams in the private report stay under NDA.
Related patterns & research
Want this engagement shape scoped for you?
Share constraints and success criteria — PoCForge will propose a human-led plan with proof and retest.