
On 8 October 2026 Citrix published critical bulletin CTX697191 and community guidance for CVE-2026-107406: a memory overflow that may lead to remote code execution or denial of service under specific SAML configurations. CVSS v4.0 base score 9.5, rated Critical. As of bulletin publication, Citrix says it is not aware of any unmitigated exploits of this vulnerability. On 9 October, NHS England cyber alert CC-4865 rated the issue High and assessed that exploitation is likely, given recent NetScaler remote code execution patterns and mass exploitation of prior flaws within hours of public details. Both statements can be true at once: treat this as an urgent patch, not as confirmed in-the-wild exploitation of 107406 itself.
What happened
| Date (2026) | Event |
|---|---|
| Thu 1 – Sun 4 Oct | CVE-2026-88779 (SAML) disclosed and fixed with 14.1-73.41 / 13.1-64.28; CISA KEV due 7 Oct |
| Wed 8 Oct | Citrix publishes CTX697191 / community guidance for CVE-2026-107406 (CVSS v4.0 9.5) |
| Thu 9 Oct | NHS England CC-4865: High severity; assesses exploitation of 107406 is likely based on recent NetScaler RCE patterns |
This is the fourth SAML-related NetScaler flaw called out in public guidance since March 2026. Edge appliances that terminate authentication keep attracting emergency upgrades measured in days, not change windows. Our earlier notes on CVE-2026-88779 and the CVE-2026-88771/88772 defender checklist still apply; this is an additional upgrade for SAML deployments, not a replacement for that work.
Who is affected
Customer-managed NetScaler ADC and NetScaler Gateway are in scope when configured as a SAML service provider (SP) or identity provider (IdP), with version-specific role requirements. Prefer Citrix’s IdP/SP split over coarser “all prior to …” summaries.
Config checks (from a configuration export, not memory):
add authentication samlAction— appliance configured as a SAML SPadd authentication samlIdPProfile— appliance configured as a SAML IdP
| Branch / edition | SAML role that is affected | Fixed build (minimum) |
|---|---|---|
| 14.1 between 14.1-73.37 and 14.1-73.41 inclusive | IdP only | 14.1-73.46+ |
| 14.1-FIPS between 14.1-73.37 FIPS and 14.1-73.41 FIPS inclusive | IdP only | 14.1-73.46 FIPS+ |
| 13.1 between 13.1-64.23 and 13.1-64.28 inclusive | IdP only | 13.1-64.29+ |
| 13.1-FIPS / NDcPP between 13.1-37.279 and 13.1-37.282 inclusive | IdP only | 13.1.37.283+ |
| 14.1 before 14.1-73.37 (and matching older 14.1-FIPS) | SP or IdP | 14.1-73.46+ / 14.1-73.46 FIPS+ |
| 13.1 before 13.1-64.23 (and matching older 13.1-FIPS/NDcPP) | SP or IdP | 13.1-64.29+ / 13.1.37.283+ |
Secure Private Access Hybrid deployments that use NetScaler instances are also affected and should move to the recommended NetScaler versions. Citrix-managed cloud services and Citrix-managed Adaptive Authentication are upgraded by Citrix; the bulletin does not require customer action for those managed services.
NetScaler ADC and Gateway 12.1 and 13.0 are end of life and do not receive security updates. Organisations on those trains must migrate to a supported fixed release.
NHS England’s affected-platform text is coarser than Citrix’s IdP/SP and build-band split. Use CTX697191 and the Citrix community guidance to decide whether a given build and SAML role are in scope; use NHS for urgency and remediation version targets, which match Citrix’s fixed list.
Why the patch churn matters
- Last week’s “fixed” IdP builds are inside this week’s IdP band. 14.1-73.41 and 13.1-64.28 (and matching FIPS) fixed CVE-2026-88779. For CVE-2026-107406 those same builds sit in the IdP-only affected range. Teams who followed the 88779 upgrade and run SAML IdP still need another jump.
- Fourth SAML-related NetScaler issue in months. Authentication-edge configuration keeps overlapping with emergency NetScaler bulletins. Inventory SAML role from config exports so you are not guessing under pressure.
- Two carefully different exploitation statements. Citrix: not aware of unmitigated exploits of CVE-2026-107406 as of bulletin publication. NHS England National CSOC: assesses it is likely this CVE will be exploited, citing mass exploitation of recent NetScaler RCEs within hours of public PoC detail. Do not invent IOCs or claim confirmed 107406 exploitation; do treat internet-facing SAML Gateways as high priority.
What to do, in order
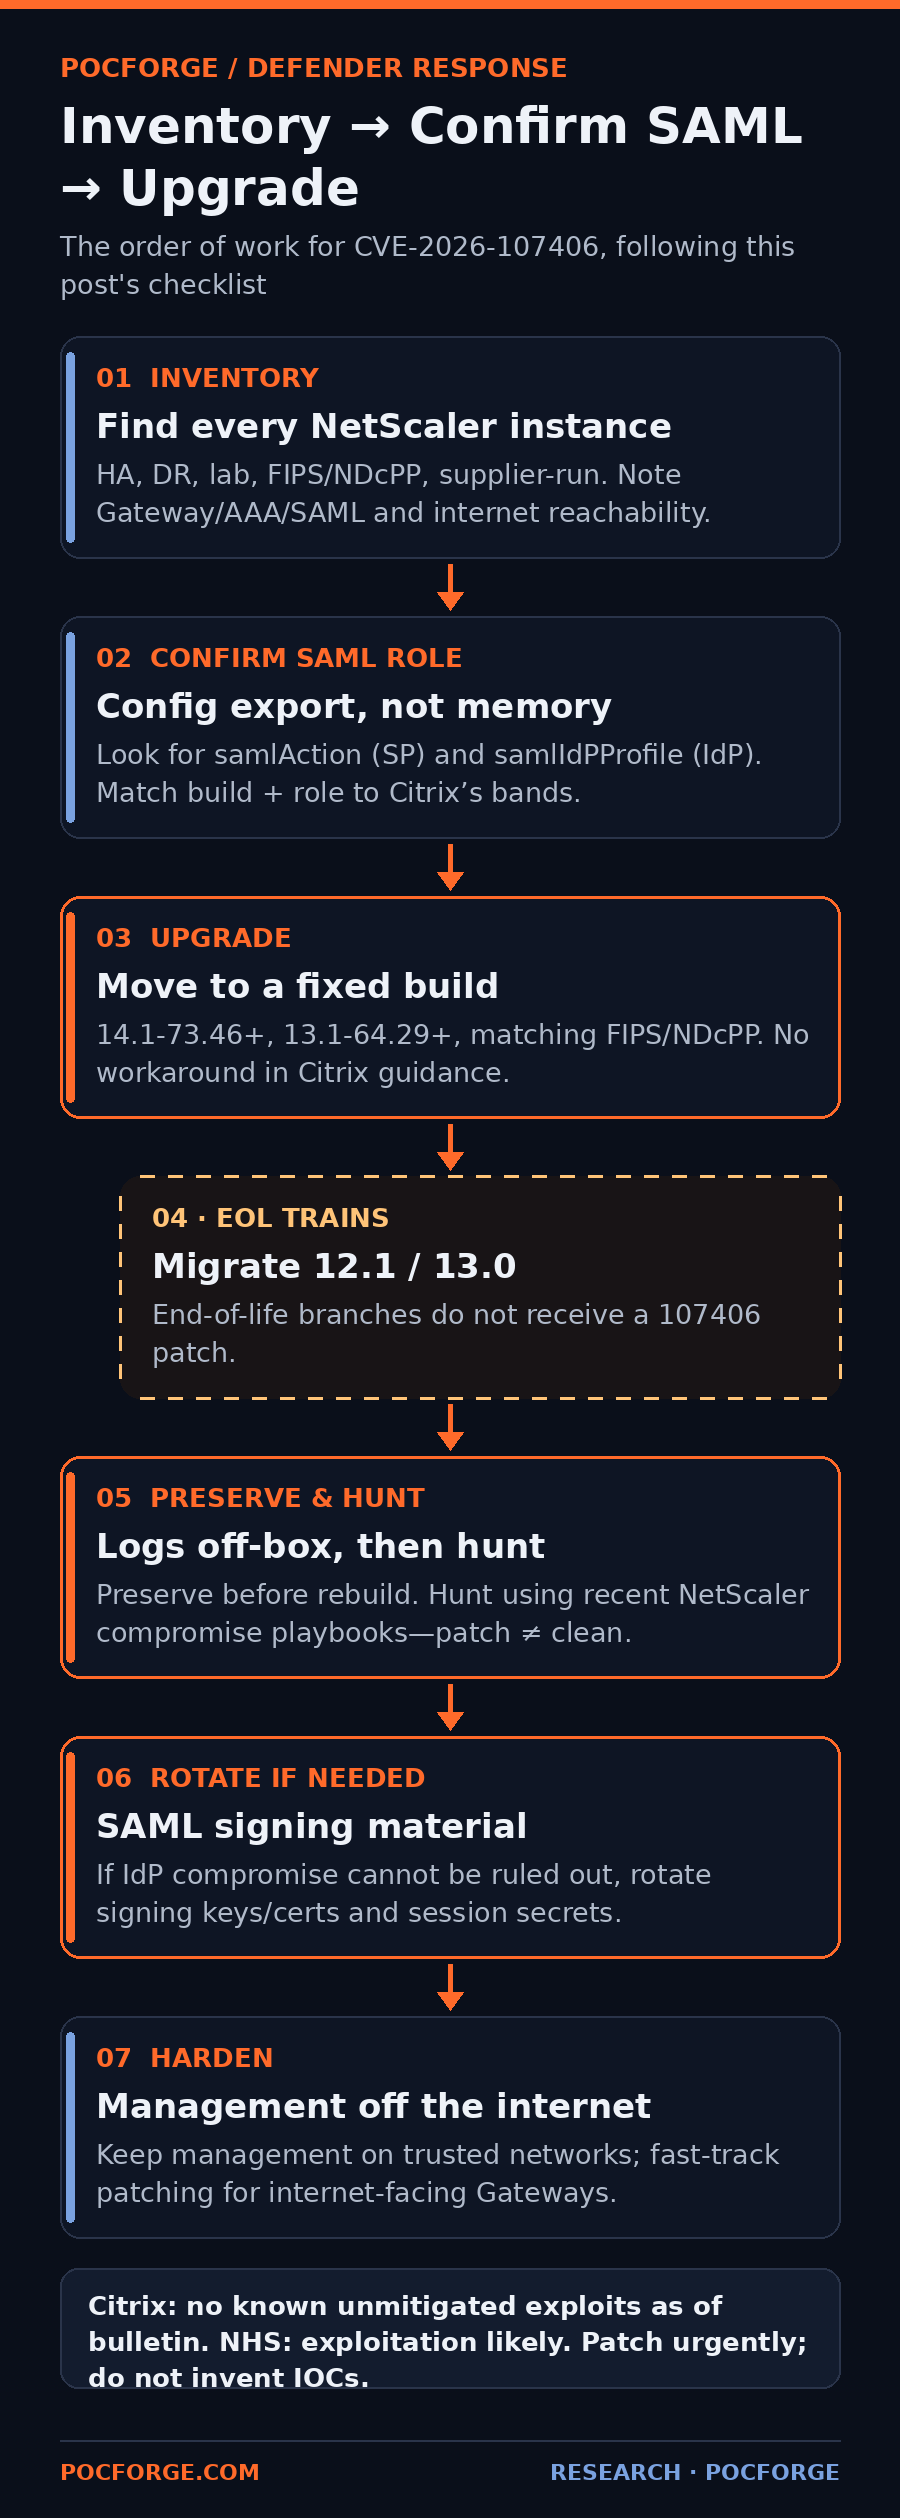
- Inventory. List every customer-managed NetScaler ADC and Gateway instance, including HA pairs, DR, lab, FIPS/NDcPP, and supplier-run appliances. Note which terminate Gateway, AAA, or SAML and which are reachable from untrusted networks.
- Confirm SAML role from a config export. Search for
add authentication samlAction(SP) andadd authentication samlIdPProfile(IdP) on each node. Record build number and role against the table above. Recollection is not evidence. - Upgrade to a fixed build. Move affected appliances to 14.1-73.46 or later, 13.1-64.29 or later, 14.1-73.46 FIPS or later, or 13.1.37.283 or later for 13.1-FIPS/NDcPP, as applicable. Treat CTX697191 as authoritative. There is no workaround listed in Citrix’s community guidance.
- EOL trains. If you are still on 12.1 or 13.0, migrate to a supported fixed release; those branches will not get a 107406 patch.
- Preserve logs before destructive changes where you can. Export appliance, authentication, HTTP, Console/telemetry, firewall/WAF, and SIEM history off-box before reimaging. An upgrade closes the hole; it can also remove the traces that tell you whether someone came through a prior NetScaler flaw.
- Hunt for compromise given recent NetScaler history. This bulletin alone does not publish a fresh public IOC set for 107406. Still review crash and reboot history, unexpected configuration changes, new accounts or sessions, unusual outbound connections from the appliance, and any open hunts from CVE-2026-88771/88772 and CVE-2026-88779. Patch does not equal clean on an internet-facing Gateway.
- Rotate SAML signing material and related secrets if IdP compromise cannot be ruled out. Where the appliance acts as an IdP, or where prior NetScaler exposure leaves uncertainty, rotate SAML signing certificates/keys, session secrets, and credentials that passed through the appliance, then re-validate downstream trust.
- Keep management off the internet. Management interfaces belong on trusted networks only. Internet-facing Gateways deserve a fast-track patch process measured in days.
Quick checklist
- Every NetScaler instance inventoried (HA, DR, FIPS, supplier-run)
- SAML SP/IdP confirmed from config export (
samlAction/samlIdPProfile) - In-scope appliances on 14.1-73.46+, 13.1-64.29+, or matching FIPS/NDcPP fixed builds
- EOL 12.1 / 13.0 migration planned or complete
- Logs preserved off-box before rebuilds
- Compromise hunt completed against recent NetScaler exposure, not only this CVE
- SAML signing material and session secrets rotated where IdP compromise cannot be excluded
- Management interfaces confirmed unreachable from the internet
How authorised VAPT helps
Internet-exposed NetScaler Gateway and AAA planes show up repeatedly in external attack-surface reviews, often because a management or authentication interface was left open “temporarily,” or because SAML was added for one application and never inventoried elsewhere. An authorised external assessment can confirm which Gateways are reachable, whether management is segmented the way you think, and whether SAML SP/IdP configuration matches the build bands in this bulletin. PoCForge does not publish exploit steps or reproduce this flaw outside authorised engagements; the useful finding is exposure and configuration inventory, not a public PoC.
Sources
- Citrix Community — Immediate guidance for CVE-2026-107406
- Citrix security bulletin CTX697191
- NHS England cyber alert CC-4865 (9 Oct 2026)
- PoCForge — CVE-2026-88779 SAML zero-day checklist
- PoCForge — CVE-2026-88771/88772 defender checklist
Frequently asked questions
We already upgraded for CVE-2026-88779. Are we done?
Not if you are a SAML IdP on 14.1-73.37 through 14.1-73.41 (or 13.1-64.23 through 13.1-64.28, or matching FIPS). Those builds fixed 88779 and sit inside the IdP-only affected band for CVE-2026-107406. Move to 14.1-73.46+ or 13.1-64.29+ (and matching FIPS).
Is CVE-2026-107406 being exploited?
Citrix stated as of bulletin publication that it is not aware of any unmitigated exploits of this vulnerability. NHS England assesses exploitation is likely based on recent NetScaler RCE mass-exploitation patterns. Neither statement is the same as confirmed public exploitation of 107406; patch urgently and hunt using your existing NetScaler compromise playbooks.
Is there a workaround?
Citrix’s community guidance does not list a workaround. Upgrade to a fixed build. Global deny lists or IP filters from prior NetScaler events are not a substitute for this fix.
How do I know if we are SP, IdP, or both?
From a configuration export, look for add authentication samlAction (SP) and add authentication samlIdPProfile (IdP). Check every node, including HA secondaries and DR.
Do Citrix-managed cloud or Adaptive Authentication need customer action?
Citrix says the bulletin does not apply to Citrix-managed cloud services or Citrix-managed Adaptive Authentication, which Citrix upgrades. Secure Private Access Hybrid using customer NetScaler instances does need the NetScaler upgrade.
PoCForge publishes offensive-security research to explain attack paths and defensive controls. This article summarises public advisories only; it is not an exploit guide and does not describe a named client engagement.
