
Cloud security assessment in India (AWS, Azure, GCP)
Assess cloud environments for identity weaknesses, insecure configuration, excessive permissions and exploitable attack paths — with clear evidence and remediation guidance for Indian product and security teams.
-
₹35,000 – ₹90,000Indicative India band, + GST
-
Scope-based quoteConfirmed during scoping
-
Retest includedIn-scope fixes checked again
-
Identity & privilege
IAM roles, policies, federation and privilege boundaries that enable escalation or lateral movement.
-
Exposure & misconfiguration
Public storage, open services, weak network controls and forgotten assets on the internet edge.
-
Attack-path outcomes
Validated paths showing how weaknesses combine — not only a list of configuration findings.
Cloud security assessment for Indian organisations
Indian startups and mid-market product companies increasingly run production on AWS, Azure or GCP. Cloud risk is rarely a single open port: it is the combination of identity, network exposure, data stores and operational shortcuts. A useful assessment explains which weaknesses are exploitable in your account layout and what to fix first.
PoCForge provides scoped cloud security assessments with human analysis and evidence. We are a boutique — transparent about what is in and out of scope — and we publish India pricing ranges on the 2026 cost guide.
What we typically test
- IAM roles, policies and privilege boundaries
- Federation, service accounts and key/credential exposure patterns in scope
- Storage, databases and publicly reachable data services
- Network segmentation, security groups / firewall rules and ingress paths
- Logging, monitoring and detective control gaps that affect incident response
- Cross-account and identity attack paths where your design includes them
- Kubernetes or container control-plane exposure when included in scope
Cloud assessments can be configuration-and-identity focused, or paired with external infrastructure penetration testing when public IPs and edge services matter to the same risk story.
Indicative India pricing
Published cloud security review band: ₹35,000 – ₹90,000 + GST, depending on account count, service breadth and depth. Multi-cloud or large organisation programmes sit higher. Confirm with a scope review via contact.
Deliverables checklist
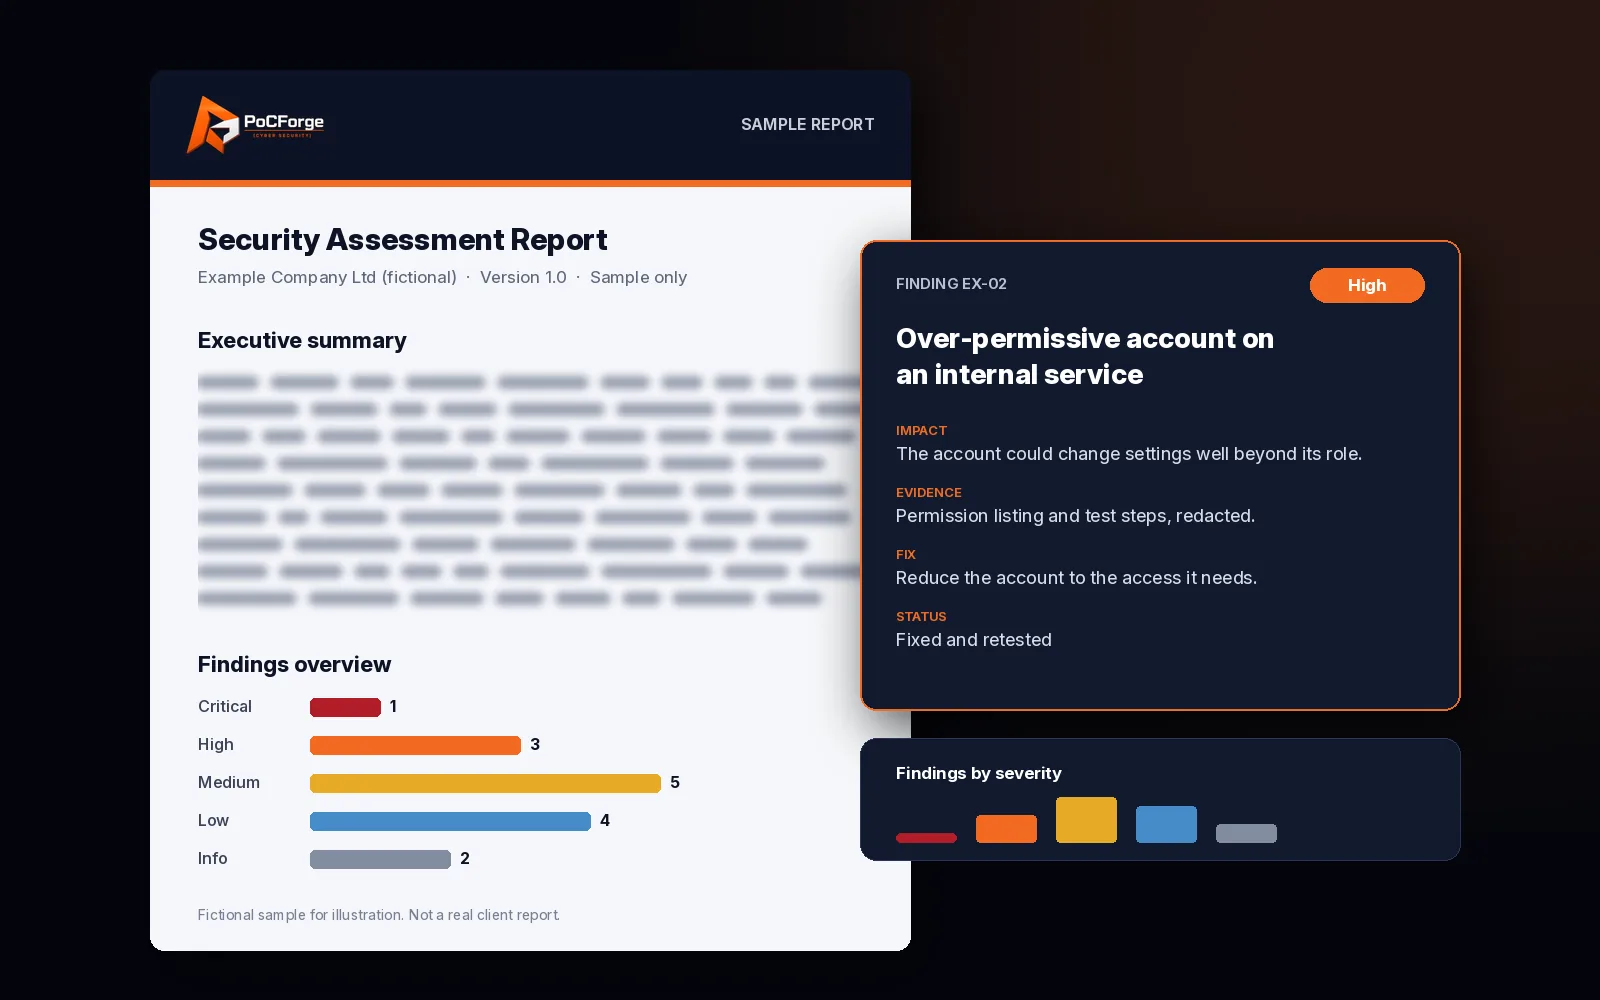
- Executive summary of cloud attack-path themes
- Prioritised technical findings with evidence
- Remediation guidance mapped to identity, network, data and detection
- Retest notes for agreed fixed items
How cloud assessment differs from a CSPM export
Cloud security posture management tools are valuable for continuous hygiene. A PoCForge assessment is not a substitute for continuous monitoring, and a CSPM CSV is not a substitute for adversarial review. We use tooling where it helps coverage, then prioritise findings that create realistic attack paths — for example an over-privileged role reachable from an exposed workload, or a public bucket that holds more than marketing assets.
Buyer checklist
- Cloud providers and account/subscription/project IDs in scope
- Whether production is included or staging mirrors are preferred
- Identity model (SSO, IAM users, workload identities)
- Crown-jewel data stores and internet-facing services
- Any compliance narrative you need the report to support (without claiming we certify you)
Who should choose a different path
If your procurement mandates a CERT-In empanelled assessor, verify the official CERT-In empanelled organisations PDF against the contracting legal entity. Quality of testing and empanelment status are related but not identical questions — see our CERT-In guide.
Outcomes you should expect
You receive validated findings, practical remediation guidance and evidence showing how identified weaknesses could affect your environment. Severity reflects real impact, and client detail stays confidential.
Typical India cloud scenarios
Early AWS account grown by engineers. A single account accumulated public buckets, broad developer IAM and a production VPC. Assessment prioritises identity and exposure before deep service-by-service trivia.
Multi-account landing zone. Shared services, logging accounts and workload accounts need path analysis across trust boundaries — not only “high” findings inside one account.
Cloud plus product security. When customer questionnaires ask about both application testing and cloud controls, pair this assessment with web or API testing so the narrative is complete.
What good cloud remediation looks like
Fix the path, not only the scanner label. Closing a public storage finding matters; removing the role that could exfiltrate after a workload compromise often matters more. Reports should help you sequence identity hardening, network exposure reduction and detective controls without pretending every medium finding is equal.
Shared responsibility — said plainly
Cloud providers secure the underlying platform; you secure identity, configuration, data and often the network design you chose. Assessments that only recite provider shared-responsibility slides without inspecting your accounts waste money. PoCForge focuses on the controls and paths you actually own inside the agreed scope, and we will say when a finding is primarily a provider-platform limitation rather than something you can patch tomorrow.
For India-market buyers comparing vendors, ask each firm: do you deliver attack-path narratives, or only tool exports? Do you include a retest? Are indicative prices published? Our ranges and process are on this site so you can compare statements of work with less ambiguity.
Sample questions we ask in scoping
- Which accounts hold production data versus experimentation?
- Who can create public resources today, and is that logged?
- Are break-glass credentials monitored?
- Which third-party integrations assume standing cloud keys?
- What does “success” look like for leadership after this assessment?
Clear answers shorten fieldwork and improve remediation workshops afterward. Reach us via contact when you are ready.
Why choose a boutique over a checklist factory
Large delivery factories can be the right fit for some procurement programmes. Boutique testing suits product companies that want senior attention on their specific architecture, clearer writing, and careful scoping. PoCForge is intentionally small: we publish prices, decline work that is a poor fit, and focus on validated impact. If you need a global brand stamp more than depth, say so — we would rather redirect you than oversell.
Frequently asked questions
How much does a cloud security assessment cost in India?
PoCForge’s indicative range is ₹35,000–₹90,000 + GST depending on accounts, services and depth. Larger multi-cloud programmes are quoted separately.
Which clouds do you assess?
AWS, Azure and GCP scopes are common. Exact services must be listed in the statement of work.
Do you need admin access?
Usually read-only auditor-style access is enough for posture and path analysis. Exploit or change actions require explicit authorisation.
Is this the same as penetration testing?
Cloud assessment emphasises identity and configuration attack paths. It can be combined with external or internal pentesting when network compromise objectives are in scope.
Can you assess Kubernetes?
Yes when the cluster control plane, workloads and identity integrations are included in scope.
How do we start?
Send provider list, account layout and goals via the contact page for a scope-based quote.
Related PoCForge guides
Need a scope-based estimate?
Share your application, infrastructure or security requirement and PoCForge will help define the right assessment.
