Sample penetration test report
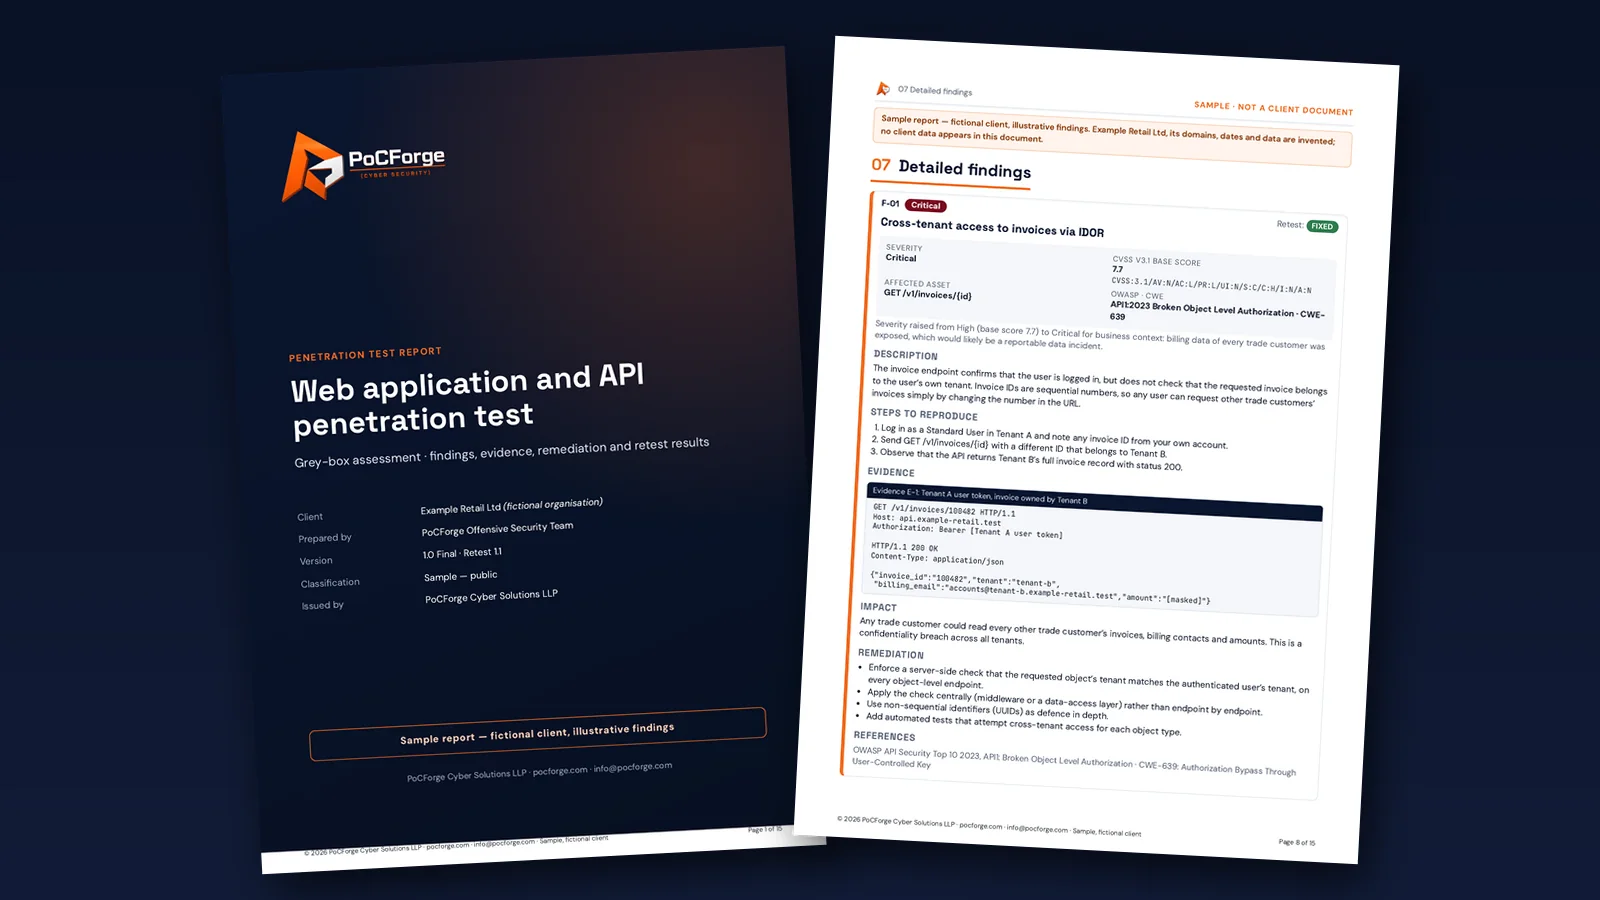
See what you receive at the end of a PoCForge test before you commit. The sample is a grey-box web application and API test for a fictional client, Example Retail Ltd, in our standard report format. Fill in a short form and we email the PDF to you.
- Fictional client, invented domains and data
- 7 findings with retest results
- Sample attestation letter
Get the report by email
What you receive
- PoCForge sample penetration test report: Example Retail Ltd, 15 pages.
- A grey-box web application and API test in our standard format.
- 7 findings with evidence, remediation and retest results, a sample attestation letter, the tools used and a glossary.
The report is sent as a PDF attachment to the work email you enter. It is not available as a public download.
Inside the report
The sample engagement is a grey-box test of a fictional retailer’s multi-tenant trade portal and its REST API, in a production-equivalent staging environment, over 6 business days. The report follows that test from scope to retest.
- Document control. Engagement details, version history, distribution, the walkthrough call and retest coverage.
- Executive summary. Overall risk, a count by severity, what it means for the business, key recommendations and positive observations.
- Scope. The web application, 62 REST API endpoints from the supplied OpenAPI specification, four test accounts across two tenants, and what was out of scope.
- Methodology. Manual grey-box testing, supported by tooling, against the OWASP Top 10 (2021), OWASP API Security Top 10 (2023) and OWASP ASVS 4.0, with PTES and NIST SP 800-115 for overall structure.
- Risk rating. CVSS v3.1 base scores adjusted for business context, with a suggested fix time for each severity.
- Detailed findings. Seven findings, F-01 to F-07, each with steps to reproduce, evidence with sensitive values masked, impact, remediation and references.
- Retest results. Each finding retested within the retest window (up to 10 issues within 6 months), with notes on what changed.
- Conclusion and appendices. A conclusion, a sample attestation letter issued by PoCForge Cyber Solutions LLP, the tools used and a glossary.
What one finding looks like
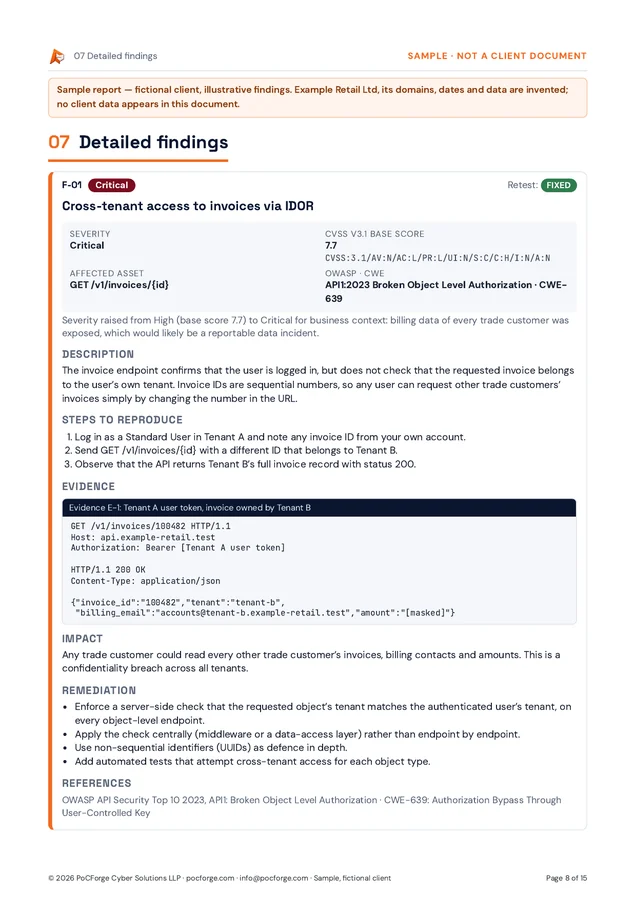
Each finding is written so an engineer can fix it and a manager can decide how urgent it is.
- Severity, CVSS v3.1 score and vector, so you can check our rating.
- CWE and OWASP mapping, and the affected asset or endpoint.
- Description and steps to reproduce, so your team can confirm the issue.
- Evidence, with identifiers, tokens and customer data masked.
- Impact, remediation and references, with fixes that address the cause.
- Retest status once you have deployed fixes.
The seven findings in the sample report
| ID | Finding | Severity (CVSS v3.1) | Retest |
|---|---|---|---|
| F-01 | Cross-tenant access to invoices via IDOR | Critical (base 7.7, raised for business context) | Fixed |
| F-02 | Privilege escalation via mass assignment of user role | High (8.8) | Fixed |
| F-03 | Stored cross-site scripting in project comments | High (7.6) | Fixed |
| F-04 | No rate limiting on login and OTP verification | Medium (6.5) | Fixed |
| F-05 | Sessions not invalidated after password change | Medium (5.9) | Not fixed |
| F-06 | Stack traces disclosed in API error responses | Low (3.7) | Not fixed |
| F-07 | Missing Content Security Policy header | Informational | Not fixed |
At retest, 4 of the 7 findings were fixed, including every Critical and High finding. The 3 open findings are lower risk and have a remediation plan.
Related
Frequently asked questions
Is Example Retail Ltd a real client?
No. Example Retail Ltd is fictional. Its domains, dates and data are invented and its findings are illustrative. The structure, level of detail and format are what you receive.
Why do you ask for my details?
So we can email the report to you. The form also tells us who asked, so we can answer questions about it.
Who issues PoCForge reports?
Reports and attestation letters are issued by PoCForge Cyber Solutions LLP, the company behind PoCForge.
Will my report look the same?
The structure is the same. The findings, evidence and recommendations are specific to your scope. For white-label engagements, the same report is issued on the partner’s template and branding.
What is the attestation letter?
A short letter that summarises the engagement and the retest outcome for third parties who need evidence of testing. It does not contain vulnerability details.
Is a retest included?
Yes. We retest up to 10 issues within 6 months of the original test and update the report.
Which CVSS version do you use?
The sample rates findings with CVSS v3.1 base scores and vectors. Where business context makes a finding more serious, the report raises the severity and says why, as with F-01.
Start with a scope review
What we need from you
- The application URL(s) and which environment we test (staging that matches production is ideal).
- Two accounts for each role in scope, and two tenants if the product is multi-tenant.
- A short list of the workflows that matter most: sign-up, payments, exports, admin, invitations.
- Known rate limits, WAF rules or change freezes we should plan around.
- A named contact who can pause testing, and the dates you need the report by.
Nothing here needs to be final. A rough answer is enough for the first call, and we confirm the details in the statement of work.
Want a report like this for your systems?
Tell us what you need tested. A tester replies with questions or a draft scope.
Request a free scope review →